This article explains how to manage user access and report permissions in Mapp Intelligence. By setting up different roles, you can control which users can view, create, and manage reports in specific categories. This guide walks you through a simple example with two users to illustrate how to configure user management efficiently.
Preface
For this example, we focus on two users who represent two broader user groups:
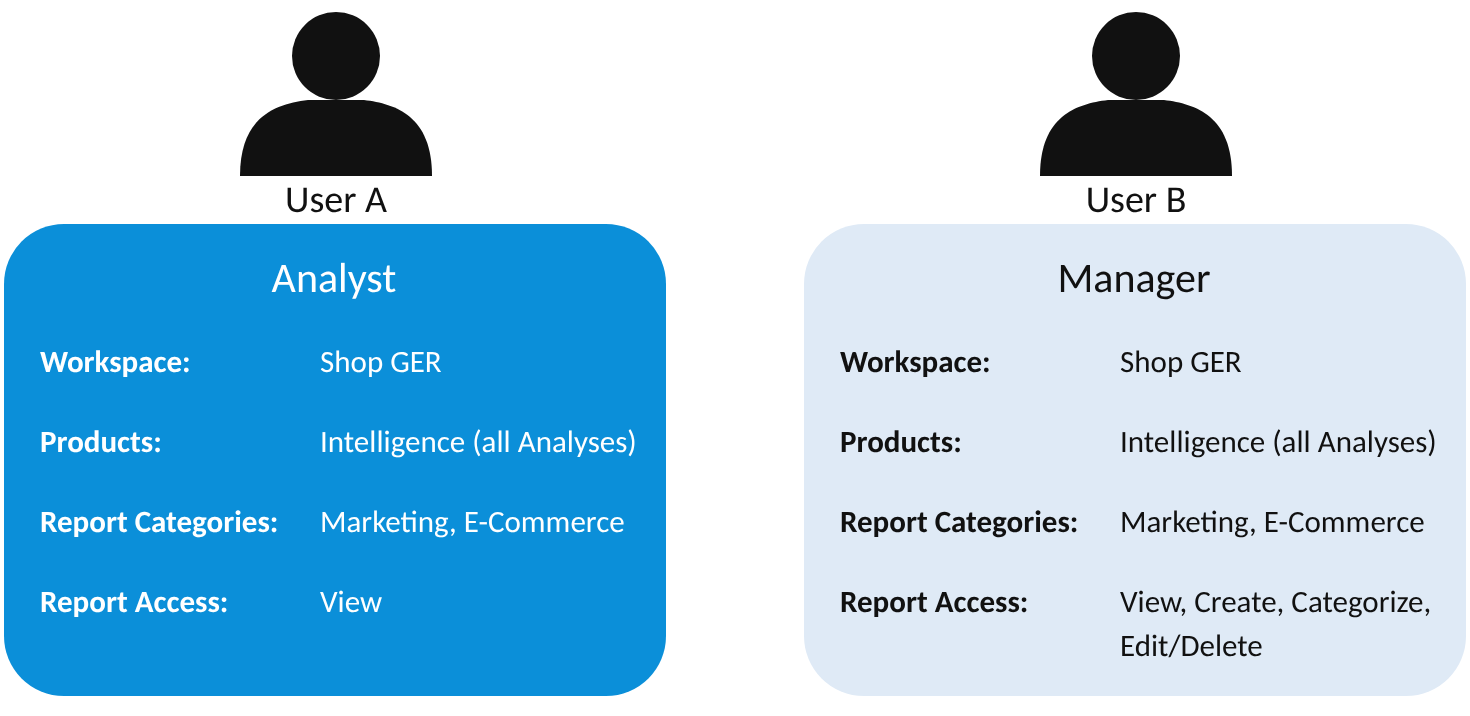
User A is an analyst and needs access to data from the German online shop ("Shop GER"). He should have full access to Mapp Intelligence and be able to view reports in the Marketing and E-Commerce categories.
User B is a manager and also needs access to Shop GER. In addition to viewing reports in Marketing and E-Commerce, he should also be able to create, categorize, edit, and delete reports.
Step 1: Setting up Users
As a first step, the logins for User A and User B need to be created. To open the User Management, click the gear icon in the top navigation bar and select User Management. Then go to Users.
.png)
Create two new users. In our example, the first name is User and the last name is A or B.
Fill in the remaining basic user information.
(Optional) Set a password expiration date.
Do not assign any roles yet.
Step 2: Setting Up Report Categories
To manage access to reports based on specific target groups, categories must be set up. This is done in Categories in the User Management.
For our example, users need access to Marketing and E-Commerce reports, so these two categories must be created. In the next step, you assign them to roles and define what users can do with the reports in them.
Step 3: Setting Up Roles
Workspace access (in our case, Shop GER), product access (in our case, Mapp Intelligence), and report rights are managed via roles. For this example, two roles must be created. This is done in Roles in the User Management.
Report access levels
The access level of a role defines what users can do with reports in the categories assigned to the role. Each level includes the permissions of the levels above it in the table.
Access level | Permissions |
|---|---|
View | Users can see reports in the assigned categories. The categories are greyed out and cannot be changed or assigned by the user. |
Create | Users can also create private reports. These reports remain private unless a category is added to them. Users cannot edit or remove categories. |
Categorize | Users can also add the assigned categories to reports, including their own, which makes these reports accessible to others. Users can also edit and delete categories. |
Edit/Delete | Users can also edit and delete reports in the assigned categories. |
Full Access | Users have all rights for every report, including private reports of other users. |
A) Creating a Role for Viewing Reports
This role is for User A.
Choose a name for the role. A name that contains the product, analysis access, workspace, categories and access level (for example, Intelligence-Full_Shop GER_Marketing_E-Commerce-View) makes roles easy to tell apart later. A description is optional.
In the Workspace assignment, assign the workspace Shop GER to the role.
In the Service assignment, select Intelligence for Shop GER in the Intelligence section.
Assign User A to the role.
In the Analyses access configuration, set the slider to Full. This grants full access to all analyses available in Mapp Intelligence.
In the Report access configuration, select Activate report access for this role and set the Access level to View.
Assign the categories Marketing and E-Commerce to the role.

Save the role.
As a result, users assigned to this role (for example, User A) can view reports in the selected categories. The categories are greyed out, and the user cannot change or assign them.
B) Creating a Role for Viewing, Creating, Categorizing, and Editing/Deleting Reports
This role is for User B. It is set up in the same way as the first role. Only these settings differ:
Choose a different role name (for example, Intelligence-Full_Shop GER_Marketing_E-Commerce-EditDelete).
Assign User B to the role.
Set the Access level to Edit/Delete.
As a result, users assigned to this role (for example, User B) can view, create, categorize, and edit/delete reports in the selected categories.